
Security Information and Event Management, or SIEM, tools are a core part of modern log management and security operations. In 2026, SIEMs are increasingly expected to ingest security telemetry from cloud services, endpoints, identities, and applications, then correlate it to help teams detect threats faster and respond with better context. With growing regulatory pressure for stronger cyber governance and incident readiness, including EU NIS2 requirements and US public company cybersecurity disclosure rules, SIEM remains a practical signal that an organization is taking monitoring, detection, and reporting seriously.
1. IBM Security QRadar

IBM Security QRadar aids security teams in detecting, assessing, and prioritizing the most critical threats to the organization. The system gathers information from assets, clouds, networks, endpoints, and users, correlates it with vulnerability and threat intelligence, and uses advanced analytics to identify and track the most serious threats as they progress through the kill chain.
Key Features:
-
IBM QRadar XDR Connect connects your tools, automates your security operations center, and simplifies procedures.
-
IBM QRadar SIEM is a security analytics tool that gives users actionable insight into your major threats.
-
IBM QRadar NDR examines your network for risks that aren't readily apparent.
Cost:
You can talk to their sales team and request a quote.
2. Splunk Enterprise Security

Splunk Enterprise Security is an analytics-driven SIEM that uses actionable intelligence and advanced analytics to battle threats at scale. Splunk is a security platform that allows you to identify, investigate, and respond in real-time to improve your security operations and reduce risks.
Key Features:
-
By absorbing data from multi-cloud and on-premises deployments, you can break through data silos and acquire actionable knowledge.
-
Gather all of the information you'll need and begin a flexible inquiry.
Cost:
You can talk to their sales team and request a quote.
3. LogRhythm NextGen SIEM Platform
LogRhythm's award-winning NextGen SIEM Platform combines comprehensive security analytics, user and entity behavior analytics (UEBA), network detection and response (NDR), and security orchestration, automation, and response (SOAR) into a single, integrated platform for rapid threat detection, response, and neutralization.
Key Features:
-
Identifying dangers, automating and cooperating on investigations, and quickly resolving concerns are key capabilities.
-
To rapidly find the answers you need and understand what's going on in your environment, search your logs and other machine data.
-
Automate time-consuming and repetitive activities so that your employees may focus on areas where their expertise can be put to good use.
Cost:
You can discuss this with their sales team and request a quote.
4. Sumo Logic

Sumo Logic invented continuous intelligence, a new product category that aids businesses of all sizes in managing the data difficulties and opportunities that digital transformation, modern applications, and cloud computing providers.
Key Features:
-
Customizable dashboards bring teams together by displaying logs, metrics, and performance data for full visibility and consistency.
-
Real-time analytics can help you discover and resolve potential cyberattacks, as well as to detect and prevent breaches and save compliance costs.
Cost:
You can discuss this with their sales team and request a quote.
5. AlienVault USM

AlienVault USM Anywhere is a cloud-based security management solution for cloud, hybrid cloud, and on-premises settings that accelerates and centralizes threat detection, incident response, and compliance management.
Key Features:
-
Examine SIEM event correlation and alerts that have been auto-prioritized.
-
Monitoring of user activity
-
Up to 90 days of searchable online events
-
Cloud intrusion detection is a service that detects intrusions in the cloud (AWS, Azure, GCP)
-
Intrusion detection in the network (NIDS)
Cost:
You can discuss this with their sales team and request a quote.
6. LogPoint

LogPoint enhances security teams' skills while assisting them in combating existing and future threats by combining smart technology with a deep understanding of customer concerns.
Key Features:
-
For comprehensive security analytics, the Log point SIEM & SOAR system collects events and incidents from billions of logs in any IT architecture of any size.
-
Logpoint UEBA examines the behavior of people and entities within your infrastructure using sophisticated Machine Learning to uncover interesting or dangerous behaviors and trends.
Cost:
You can discuss this with their sales team and request a quote.
7. Microsoft Azure Sentinel
With SIEM redesigned for the modern world, Microsoft Azure Sentinel allows you to see and stop threats before they cause harm.
Key Features:
-
Collect data at the cloud-scale, including data from all users, devices, apps, and infrastructure, both on-premises and across various clouds.
-
Detect previously unknown attacks and reduce false positives with Microsoft's unrivaled threat intelligence and analytics.
-
With built-in orchestration and automation of typical processes, you can respond to events quickly.
Cost:
You can discuss this with their sales team and request a quote.
8. Rapid7 InsightIDR

Rapid7 InsightIDR is a SaaS SIEM that detects and responds to contemporary threats. By combining disparate data sources, providing early and reliable out-of-the-box detections, and giving rich visual investigations and automation to expedite a response, InsightIDR enables security analysts to work more efficiently and effectively.
Key Features:
-
Detection and Response to Endpoints (EDR)
-
Analyze Network Traffic (NTA)
-
Integrations with the Cloud
Cost:
The cost for InsightIDR Advanced starts at $5.61/mo per asset.
9. McAfee Enterprise Security Manager

McAfee Enterprise Security Manager is a security information and event management (SIEM) solution that helps evaluate, analyze, and respond to cyber threats by providing intelligence information and integrations.
Key Features:
-
Access unsurpassed security and efficiency for your entire organization.
-
Whether on-premises or in the cloud, keep your email infrastructure and users safe.
-
With a live, learning solution, you can protect your networks, servers, and data centers.
Cost:
You can discuss this with their sales team and request a quote.
10. Datadog

Datadog helps businesses of all sizes and industries with digital transformation and cloud migration by facilitating collaboration between development, operations, security, and business teams, reducing application time to market, securing applications and infrastructure, understanding user behavior, and tracking key business metrics.
Key Features:
-
An application's performance shoKey featured be monitored, troubleshot, and optimized.
-
Quickly search, filter, and analyze your logs for troubleshooting and open-ended data study.
-
On a single platform, end-to-end visibility of the user experience.
Cost:
The tool offers a free trial after which one can opt for it at $ 0.20 Per GB of analyzed logs, per month. It can also be billed annually or $0.30 on-demand.
11. Blumira cloud SIEM platform

Thanks to automated threat detection and response, Blumira's cloud SIEM platform enables organizations of any size to more effectively battle cybersecurity attacks in near real-time.
Key Features:
-
Full access to assistance and longer data retention.
-
Coverage indeed expanded to include popular cloud applications.
-
Your entire working environment will be covered.
Cost:
The tool offers a wide range of pricing options to choose from ranging from a free trial to an Advanced level. For Microsoft 365, you have to pay $8/User, Per Month; Cloud costs $12/User, Per Month; and the Advanced option costs $16/User, Per Month.
12. Logz.io

Logz.io is a leading cloud-native observability platform that lets engineers use the best open-source tools without having to manage, scale, or operate them.
Key Features:
-
Automatically parse and index your logs for analysis at any scale with our fully managed ELK Stack.
-
On Prometheus, you can collect, store, and analyze metrics without having to worry about the backend.
-
Security concerns are detected and investigated using a fully instrumented system.
Cost:
The tool offers three pricing options: Community which is free of cost. Pro is available at $0.92, and for the Enterprise option, one has to ask the sales team for a quote.
13. Graylog

Graylog is a prominent centralized log management solution that uses open standards to capture, store, and analyze gigabytes of machine data in real-time.
Key Features:
-
Create custom dashboards quickly and easily to see a wide range of metrics and trends on a single page.
-
Fault tolerance is incorporated into the product and ensures dispersed, load-balanced functioning without the need for extra components.
Cost:
You can talk to their sales team and request a quote.
14. FortiSIEM

From IoT to the cloud, FortiSIEM provides a comprehensive, holistic, and scalable solution for security, performance, and compliance management to enterprises of all sizes.
Key Features:
-
Adding virtual machines (VMs) is a simple way to boost performance and log-processing capacity.
-
Businesses can limit what each individual has access to through role-based access control, which can be customized.
-
Using FortiSIEM Analytics, you can find threats and indicators of compromise (IOC).
Cost:
You can talk to their sales team and request a quote.
15. Juniper Secure Analytics

Juniper Secure Analytics is a business security information and event management (SIEM) system that collects massive amounts of event logs from thousands of devices, endpoints, and applications in real-time based.
Key Features:
-
A physical security information and event management (SIEM) appliance that collects, analyses, and consolidates security data from globally networked devices to quickly detect and correct security incidents.
-
Using big data analysis, summarises the data into a useful list of transgressions, speeding up investigations and remediation.
Cost:
You can talk to their sales team and request a quote.
16. EventSentry
EventSentry is a hybrid SIEM solution that provides customers with a holistic picture of their servers and endpoints by combining real-time (event) log monitoring with full system health and network monitoring.
Key Features:
-
Filter thresholds let you know when a certain number of events happen in a certain amount of time.
-
With Event Log Consolidation, all or some event log entries are stored in a central database.
Cost:
You can talk to their sales team and request a quote.
17. Advanced Security Manager by Cisco

Advanced Security Manager by Cisco is a computer security tool that protects data from unauthorized access.
Key Features:
-
The tool enables consistent policy enforcement
-
Enhances process compliance and error-free deployments
-
Improves ability to monitor security threats
Cost:
You can talk to their sales team and request a quote.
18. Micro Focus ArcSight Enterprise Security Manager (ESM)
ArcSight Enterprise Security Manager (ESM) is a SIEM platform that drastically decreases the time it takes to mitigate cyber-security threats by combining threat detection, analysis, triage, and compliance management.
Key Features:
-
With sophisticated and adaptable SIEM correlation analytics, you can reduce threat exposure by detecting threats in real-time.
-
ArcSight's native SOAR automates reaction, saving your analysts time and enhancing operational efficiency.
-
Increase your SOC's return on investment with a SIEM that improves visibility and interacts with your existing ecosystem.
Cost:
You can talk to their sales team and request a quote.
19. OSSIM (Open Source)
Alienvault OSSIM is an open-source SIEM product that helps users boost security visibility and control in their networks by contributing and receiving real-time information about hostile hosts.
Key Features:
-
Threat detection and incident response in the cloud, on-premises infrastructure, and cloud apps are all centralized.
-
For constant compliance and forensics investigations, log management is essential.
-
Advanced threat detection with prioritized alarms in real-time and few false positives.
Cost:
You can talk to their sales team and request a quote.
20. Panther

Panther empowers security teams to detect any breach at, anytime and is widely accepted by customers.
Key Features:
-
With zero-ops and cloud-first workflows, you can process and preserve all of your security data.
-
Detect suspicious behavior across your entire area as soon as it occurs.
-
With Python, version control, unit tests, and CI/CD, you can create a high-fidelity alerting pipeline.
Cost:
You can talk to their sales team and request a quote.
21. SmartEvent event management
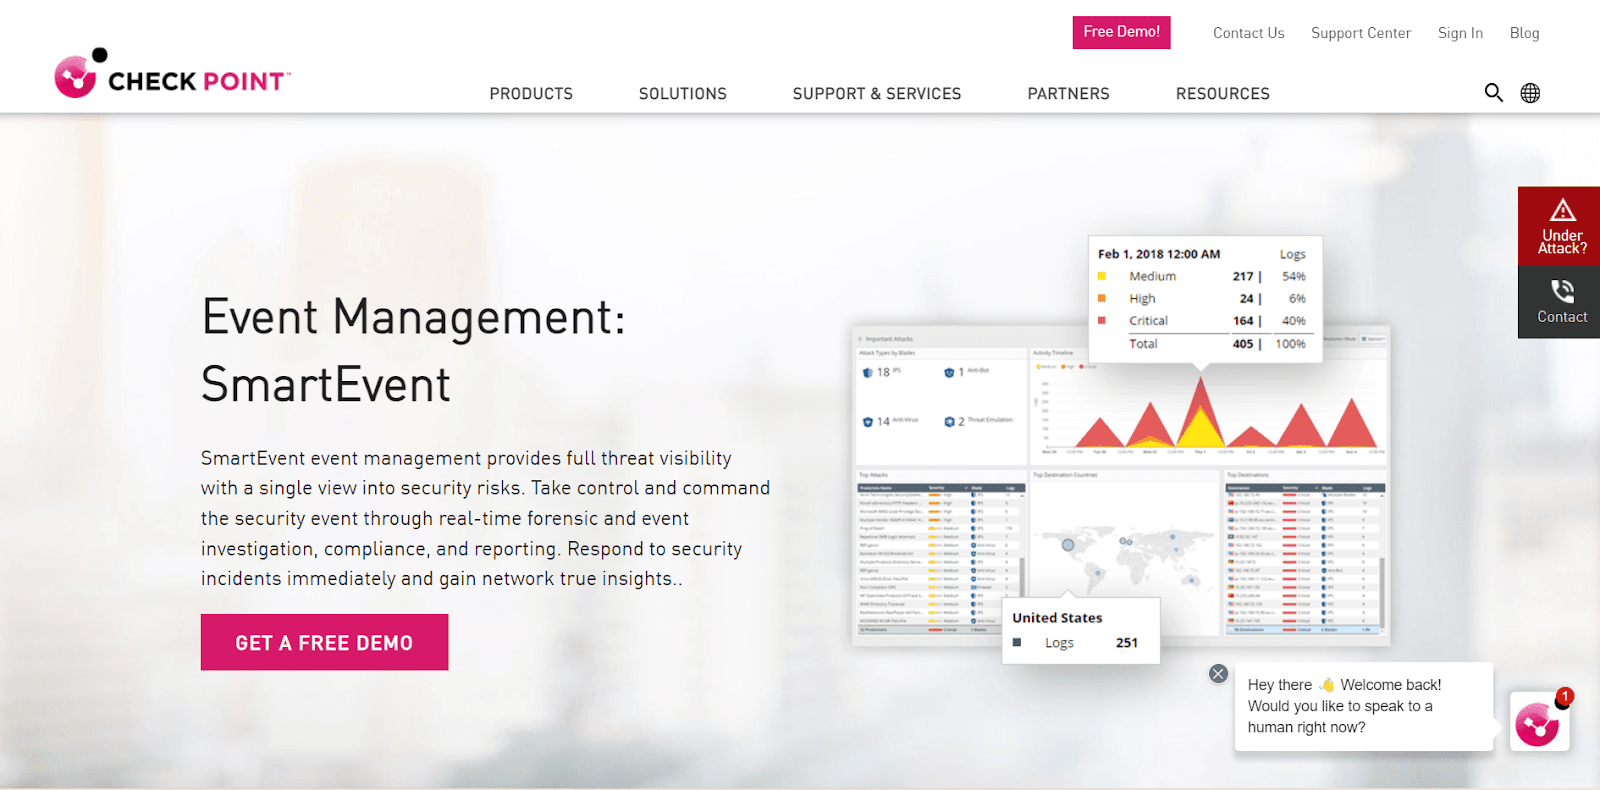
SmartEvent event management gives you a single view of your security threats and gives you complete threat visibility.
Key Features:
-
Using genuine forensic and event investigation, adherence, and reporting, you may take command and control of the security situation.
-
Respond quickly to security problems and receive actual network information.
Cost:
You can talk to their sales team and request a quote.
22. Next-Gen SIEM from Logsign
Logsign specializes in automation-driven cyber security solutions and is dedicated to providing the smartest, most user-friendly, and most cost-effective cybersecurity detection and response systems and value-added services available.
Key Features:
-
Based on the Mitre Att&ck framework, real-time detection, and prevention, as well as a large correlation library.
-
Real-time monitoring, pre-defined dashboards, reporting, and adherence to regulations (PCI DSS, ISO 27001, HIPAA, SOX, and more).
-
Notifications and actions are both automatic.
Cost:
You can talk to their sales team and request a quote.
23. Securonix Security Operations

With actionable security intelligence, Securonix is trying to drastically improve all aspects of data security.
Key Features:
-
Smart analytics relieves analysts of their workload and reduces false positives.
-
With a common platform, you may simplify your infrastructure.
-
With immediate deployment and an easy user interface, you may achieve a quick time to value.
Cost:
You can talk to their sales team and request a quote.
24. Devo

Devo helps the world's most instrumented businesses realize the full value of machine data by putting more data to work right now.
Key Features:
-
Without re-architecting, No-Compromise Architecture frees IT from the unpleasant limits of traditional enterprise log management (ELM) systems, allowing it to consume petabytes of data every day at breakneck speed.
-
For fully contextual analytics, Devo blends real-time feeds with historical data.
Cost:
You can talk to their sales team and request a quote.
25. Exabeam Security Management

Exabeam is a security information and event management (SIEM) solution that helps security operations and insider threat teams work smarter by identifying, investigating, and responding to cyberattacks in 51% less time.
Key Features:
-
Combine all of your security information into one view.
-
By eliminating false positives, the detection system can help you in improving productivity.
-
Detect dangers that other solutions miss using market-leading behavioral analytics.
Cost:
You can talk to their sales team and request a quote.
26. Snare

When it comes to tackling log collection and management difficulties, Central Snare can help you save time, and money, and reduce risk.
Key Features:
-
Logs can be found in a variety of places.
-
Events and logs should be filtered to remove noise.
-
You can choose which data goes to which place.
-
Any device's Syslog feed can be consumed.
Cost:
You can talk to their sales team and request a quote.
27. FireEye Helix

FireEye Helix is an intelligence-driven platform that makes security operations easier to manage, integrate, and automate.
Key Features:
-
FireEye Helix's security analytics leverage machine learning and artificial intelligence to establish a baseline for your firm's "typical" behavior and generate warnings when anomalies or deviations happen.
-
By correlating incident data and applying unparalleled frontline intelligence and analytics, FireEye XDR uncovers risks.
Cost:
You can talk to their sales team and request a quote.
28. BMC AMI Command Center for Security

The BMC AMI Command Center for Security is a cost-effective SIEM (Security Information and Event Management) system for z/OS.
Key Features:
-
The mainframe activity linked to system-wide security is displayed on a pre-configured dashboard.
-
BMC Helix can be used to provide alerts for visibility, ticket creation, and issue response coordination.
-
For enterprise-wide intelligent event correlation, scan and highlight issues in subsystems.
Cost:
You can talk to their sales team and request a quote.
29. ManageEngine Log360
ManageEngine Log360 aids in the security of your IT environment by detecting and alerting you to unauthorized network security modifications.
Key Features:
-
Logs should be collected from end-user devices, servers, network devices, firewalls, antivirus, and intrusion prevention systems, among other places.
-
Use key information from numerous security incidents to identify security dangers.
Cost:
You can talk to their sales team and request a quote.
30. WhiteRock Cybersecurity
WhiteRock Cybersecurity is a 24-hour, seven-day-a-week service that includes threat detection, remediation help, compliance, SIEM, and log management.
Key Features:
-
It comes with a built-in thread detection and identification scanner.
-
It can provide solutions to the threats it has in its database.
Cost:
You can talk to their sales team and request a quote.
Things to keep in mind while choosing Security Information and Event Management (SIEM) tools
SIEM products share a few common traits. They gather information from a variety of sources (including threat intelligence), evaluate it, provide warnings, perform analytics, and present a historical overview or summary. Of course, when it comes to selecting a SIEM security solution, each company will have its own set of criteria for determining whether a tool's capabilities match its requirements. This will be determined by criteria such as the size of the company, the sorts of data it holds, the vendors it interacts with, the regulatory frameworks it operates under, the budget it has available, and, of course, the usability preferences of the IT team.
Here are a few things to consider before getting one:
Will the tool genuinely help you collect logs better?
This is a simple but critical step since you want software that will help you collect and manage logs more efficiently. Look for compatibility across systems and devices, and a dashboard with user-friendly features never hurts.
Is the tool going to help you reach compliance?
Look for a technology that makes auditing and reporting easier. You should be concerned about compliance even if you aren't right now. A SIEM tool can help you improve your performance in this area.
Is your threat response workflow set up to aid in the management of previous security incidents?
One of the most important features of a SIEM tool is that it allows you to get a quick summary of previous events, assess what happened, and teach the system to use historical patterns to guide future action. Look for capabilities that allow you to drill deep into your data.
Is the tool capable of providing you with the quick, accurate, and automated responses you require?
First and foremost, event response time must be adequate.
Customizable security alarms can also make your life a lot easier. You want to be able to walk away without worrying about missing something important. Ensure that alerting is a top priority in the tool.
Conclusion
In 2026, SIEM is most valuable when it functions as a security system of record that unifies logs, enriches them with threat intelligence, and supports investigations, compliance reporting, and faster response. The best fit depends on your environment and operating model, including cloud footprint, log volume, required retention, detection content quality, and how well the tool integrates with SOAR and XDR workflows. A strong SIEM will not eliminate all risk, but it can significantly improve visibility, shorten investigation time, and help security teams prove control maturity when auditors and regulators come knocking.
FAQ
What is the purpose of the SIEM tool?
SIEM is essential since it makes it easier for management to take security by filtering large volumes of data and prioritizing security alerts generated by the program.
What is the SIEM implementation process?
A successful SIEM deployment should include the following major components or important functions: Log and event management, as well as data aggregation.
Why is SIEM so costly?
SIEM expenses, in particular, are numerous and varied. Initial licensing costs, deployment, ongoing maintenance, renewal, data source integration, and personnel training to effectively run the SIEM are all factors to consider.
What is the definition of SIEM deployment?
SIEM (Security Information and Event Management) technologies are an important aspect of every contemporary enterprise's information security policy, but getting the most out of one requires careful planning and execution.
Is SIEM a virus scanner?
SIEM is similar to anti-virus in that it is frequently used to detect threats to your environment and serves as one of the many levels of security that examines both end-points and the entire environment. Threats emerge and alter all the time, and SIEM systems must be able to respond to these changes.
