
Static code analysis is the process of examining source code without running it to identify security flaws, reliability bugs, and maintainability issues as early as possible. In 2026, this matters more than ever because software teams are producing code at huge scale, increasingly with AI assistance, and small issues can quickly propagate across services and repositories. Large real world analyses show how common these problems remain, including findings of about 2,100 reliability issues per million lines of code across billions of lines analyzed. Static code analysis tools help development and QA teams enforce secure coding standards, reduce regressions, and keep delivery fast by catching issues directly in the IDE, pull request, and CI pipeline.
1. Raxis
Raxis outperforms automated tools, which frequently produce false results, wasting time and effort. Raxis determines the best amount of time for your company's code and assigns a security-focused former developer to analyze it for both general security and business-logic vulnerabilities.
Key Features:
-
Raxis communicates with you throughout the code review to ensure that your input is used, and they provide a report that details each finding with screenshots and remediation advice.
-
A high-level summary for management as well as a debriefing call is also included.
Cost:
You can request a quote on their website.
2. SonarQube
SonarQube is a well-known name in code quality and security, enabling all developers to write cleaner and safer code.
SonarQube is your teammate to enhance your development workflow and guide your teams, with thousands of automated Static Code Analysis rules in more than 25 programming languages and direct integration with your DevOps platform.
Key Features:
-
SonarQube integrates with your existing tools and alerts you when the quality or security of your codebase is jeopardized.
-
Reduces complexity, potential vulnerabilities, and code duplications, extending application life.
-
Focuses on more than just bugs and complexity, and provides additional features to assist programmers in writing code, such as coding rules, test coverage, de-duplications, API documentation, and code complexity, all from a dashboard.
Cost:
SonarQube has a free version and a free trial period. SonarQube's paid version begins at US$150.00 per year.
3. PVS-Studio

PVS-Studio is a technique for finding bugs and security flaws in program source code written in C, C++, C#, and Java. It is compatible with Windows, Linux, and macOS. It can be integrated into Visual Studio, IntelliJ IDEA, and other popular IDEs. The analysis results can be imported into SonarQube.
Key Features:
-
Digital reference guide for all analytic rules, locally available, on their website, and as a single document.
-
Automatic (incremental) analysis of individual files immediately the following recompilation in the IDE.
-
Simple navigation through the code's warnings.
Cost:
You can request a quote on their website.
4. DeepSource
During code reviews, DeepSource can help you automatically find and fix issues in your code. It is compatible with Bitbucket, GitHub, and GitLab accounts. This tool detects and reports anti-patterns, bug risks, and performance issues. DeepSource also generates and tracks metrics such as dependency count, documentation coverage, and so on.
Analyzers can detect file-level issues (such as an anti-pattern discovered in a specific location) as well as repository-level issues (such as four dependencies discovered that do not appear to be installed). DeepSource Autofix suggests fixes for detected issues and generates a pull request with the recommended changes.
Key Features:
-
Developers will have no trouble setting up or using the tool because it does not require complex build pipeline configuration and integrates natively with GitHub, GitLab, and Bitbucket.
-
DeepSource can also generate fixes for some of the most common issues it encounters and format your code automatically.
-
DeepSource is free for open-source initiatives and smaller clubs to use.
-
It provides a self-hosted deployment option for businesses.
Cost:
The package starts at $8 per month.
5. Embold
Embold is a general-purpose static analyzer that assists developers in identifying critical code issues before they become stumbling blocks. It is the ideal tool for efficiently investigating, diagnosing, transforming, and maintaining your application software.
With the integration of A.I. and machine learning technologies, Embold will look at multiple problems at once, advise on the best way to solve them and re-factor application software as needed. Run it alongside your existing Dev-Ops stack, on-premises or in the cloud, privately or publicly.
Key Features:
-
It prioritizes hotspots in the code automatically and provides clear visualizations. It analyses software from multiple lenses, including software design, using its multi-vector diagnostic technology, and enables users to manage and improve software quality transparently.
-
Embold can be run in the cloud, or for IntelliJ IDEA users, a free plugin can be downloaded and installed directly in your IDE.
-
Users can access relevant recommendations and carry on with their work in an efficient manner thanks to the built-in AI.
Cost:
The package starts from $40 per month.
6. SmartBear Collaborator
SmartBear Collaborator is a code review tool that works well for both remote and co-located teams. It has extensive review capabilities for reviewing a wide range of documents, including design, requirements, documentation, user stories, test plans, and source code.
It includes electronic signature features for proof of review. It generates detailed reports. Businesses of any size can use the tool.
Key Features:
-
SmartBear has many more features, such as defect tracking and management, customizing review templates, collaborating on software artifacts and documents, and so on.
-
It is compatible with GitHub, GitLab, Bitbucket, Jira, Eclipse, Visual Studio, and other tools.
Cost:
It is free to try, and the price for a 5-user pack starts at $554 per year.
7. CodeScene Behavioral Code Analysis

CodeScene prioritizes technical debt and code quality issues based on how the organization works with the code. As a result, CodeScene limits the results to information that is relevant, actionable, and directly translates into business value.
Key Features:
-
CodeScene also goes beyond traditional tools by measuring the organization and people side of your system can detect cooperative bottlenecks in the software architecture, off-boarding risks, and gaps in knowledge.
-
Eventually, CodeScene incorporates into your CI/CD piping system to act as an extra member of the team that predicts shipping risks and provides context-aware quality gates to monitor the health of your code.
Cost:
Pricing for CodeScene begins at $99.00 per feature, per month. There is a free version available. CodeScene provides a free trial period.
8. Reshift
Reshift is a software platform as a service (SaaS) that integrates seamlessly into the software development workflow, allowing organizations to continuously deploy secure software deliverables without slowing down their pipeline.
Reshift reduces the cost and time it takes to find and fix vulnerabilities, identify potential data breaches, and assist software companies in meeting compliance and regulatory requirements.
Key Features:
-
Lowering the cost and time it takes to find and fix vulnerabilities, identifying the potential risk of data breaches, and assisting software companies in meeting compliance and regulatory requirements.
-
Redshift assists businesses in overcoming this barrier by offering a cloud-based suite of information management, handling, and analytics tools.
-
It offers a level of agility and efficiency that other types of data warehouses or infrastructures cannot match.
Cost:
You can start small with Amazon Redshift at $0.25 per hour and scale it up to petabytes and thousands of users simultaneously.
9. RIPS Technologies
RIPS is the only static analyzer solution that conducts language-specific security analysis. It finds the much more complicated known vulnerabilities deep within the programming language that no other tool can find.
Key Features:
-
It supports major frameworks, SDLC integration, and industry standards, and it can be deployed as self-hosted software or as software-as-a-service.
-
RIPS is an excellent choice for analyzing Java and PHP applications due to its high accuracy and lack of false-positive noise.
Cost:
The package starts at $48 per year.
10. Veracode
Veracode is a widely known static code analysis tool that focuses solely on security issues. This tool performs code checks across the pipeline to detect security flaws and includes IDE scans, pipeline scans, and policy scans as part of its service. As part of the program, it generates a code assessment for audit.
Key Features:
-
Static Analysis IDE by Veracode Scan intercepts security flaws in your code and offers experiential mitigation advice to help you address problems in seconds, correct them in your IDE.
-
This powerful solution will "Veracode Static Analysis IDE Scan" your code and simplify your work.
Cost:
The package starts from $690 per year.
11. Fortify Static Code Analyzer

HP Fortify is a tool that allows a developer to create error-free and secure code. This tool could be used by both developments of security teams to find and resolve security-related problems.
Key Features:
-
While searching the code, it ranks the issues discovered to ensure that the most critical ones are addressed first.
-
Fortify Static Code Analyzer (SCA) analyses an application's source code for exploitable vulnerabilities using multiple algorithms and a large knowledge base of secure coding rules.
-
To identify and remediate vulnerabilities, this technique examines every possible path that execution and data can take.
Cost:
The package starts at $948 per year.
12. Parasoft

Without a doubt, one of the best tools for Static Analysis Testing is Parasoft. This is distinct from other static analysis tools in that it can support a variety of static analysis techniques such as Pattern Based, Flow-Based, Third Party Analysis, Metrics, and Multivariate Analysis.
Key Features:
-
An advantage of the tool is that, in addition to detecting defects, it also includes a feature for defect prevention.
-
Their automated software testing tools are powered by AI and machine learning to provide you with smart recommendations and deep insight for addressing software quality.
Cost:
You can request a quote on their website.
13. Coverity

Coverity Scan is a cloud-based expansive tool. It is compatible with projects written in C, C++, Java C#, or JavaScript. This tool provides a comprehensive identification and characterization of the issues, allowing for quicker resolution. If you're looking for an open-source tool, this is a good option.
Key Features:
-
Coverity is a static analysis (SAST) solution that assists development and security teams in addressing security and quality defects early in the software development life cycle (SDLC), tracking and managing risks across the application portfolio, and ensuring compliance with security and coding standards.
-
A good text editor is capable of doing more than just inspecting and verifying a single programming language.
Cost:
According to our research, Coverity costs approximately $12k USD per year for 5 users.
14. CAST
Irrespective of the size of the project, the CAST automated tool that can analyze more than 50+ languages performs admirably. Furthermore, it provides users with a Dashboard that aids in the measurement of quality and productivity.
Key Features:
-
The product is good because it makes it easy to find problems in the code.
-
CAST AIP provides a distinct weighted (by functional throughput) perspective on areas with higher levels of technical debt. Its numerous features allow for great flexibility while necessitating a relatively steep learning curve and increasing potential failure points.
Cost:
The package starts at $20,000 per month.
15. CodeSonar
Grammatech created CodeSonar. It assists the developer in discovering errors in their program as well as errors related to domain coding. This feature is supported by no other Static Code Analysis Tool, which is a significant accomplishment in and of itself. This is a fantastic Static Code Analysis Tool for detecting security flaws and detecting errors from the ground up. For this, CodeSonar stands out as one of the best static analysis tools available in the software environment.
Key Features:
-
Remove any security flaws.
-
Identify and fix multicore / multithread flaws.
-
Customized reports improve code quality and transparency.
-
Code should be checked against coding standards and regulatory requirements.
-
Using code visualization, you can gain a better understanding of the system.
Cost:
CodeSonar 3.3 will be priced similarly to CodeSonar 3.2, which is currently available for $4,000 USD for small projects.
16. Understand

This tool, as the name suggests, helps users UNDERSTAND code by analyzing, measuring, visualizing, and maintaining it. This enables rapid analysis of large amounts of code. This is a tool that is primarily used in the aerospace and automotive industries. Supports major programming languages such as C/C++, ADA, COBOL, FORTRAN, PASCAL, Python, and others.
Key Features:
-
Understand is a programmable integrated development environment (IDE) that allows for static code analysis using a variety of visuals, documentation, and metric tools.
-
It was created to assist software developers in comprehending, maintaining, and documenting their source code.
-
It facilitates code comprehension by displaying relationship flow charts and constructing a dictionary of variables and procedures from provided source code.
Cost:
You can request a quote on their website.
17.;Code Compare

Code Compare is a tool that allows you to combine and compare files and folders. The majority of experienced developers use this tool to combine problems and deploy source changes to the system. Most popular tools, such as Mercurial, SVN, Perforce, TFS, and Git, were merged with a Code Compare tool. Code Compare is a free comparison tool that allows you to compare and merge files and folders.
Key Features:
-
TFS, SVN, Git, Mercurial, and Perforce are just a few of the popular source control systems that Code Compare integrates with.
-
Code Compare is available as a standalone file diff tool as well as a Visual Studio extension.
-
Semantic Source Code Comparison
-
Folder Comparison
-
Visual Studio Integration
Cost:
The package starts at $69.95 per month.
18. Visual Expert
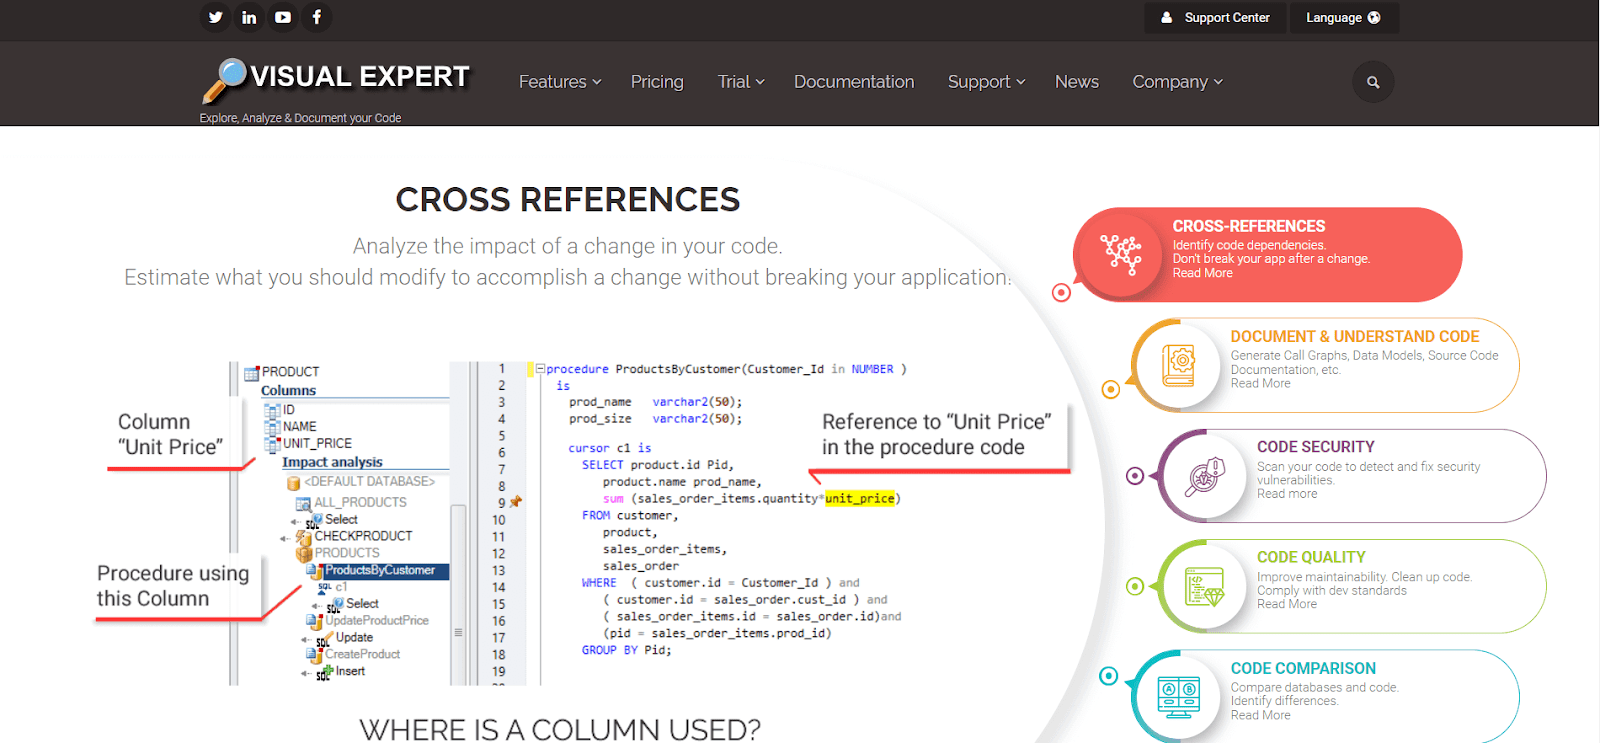
Visual Expert is a one-of-a-kind static code analysis tool for SQL Server, Oracle, and PowerBuilder.
Key Features:
-
Visual Expert is an Oracle PL/SQL, SQL Server T-SQL, and PowerBuilder static code analyzer.
-
E/R Diagrams synchronized with code view.
-
Code Performance Analysis
-
Identify code dependencies so that you can change your code without breaking your application.
-
Code exploration
-
Source Code Documentation
-
Hundreds of features can be used to improve the quality, performance, and security of your applications.
Cost:
The package starts at $495 per year.
19. Clang Static Analyzer

Clang Static Analyzer is an open-source tool for analyzing C and C++ code. It makes use of the clang library, resulting in a reusable component that can be used by multiple clients.
Key Features:
-
The Clang Static Analyzer is a system software analysis tool that detects application bugs. It is open-source and extensible.
-
It has been implemented as a library for easy-to-use project analysis. Simply add the library to your project.
-
A command-line utility that allows users to run the static analyzer against their codebase as part of a regular build (from the command line).
-
This works by running the compiled files through the analyzer, and the results are displayed in the web browser once the build is complete.
Cost:
You can request a quote on their website.
20. CppDepend
When tried to compare to other static analysis tools, CppDepend is very simple to use. This tool is used to analyze C/C++ code, as the name implies. Supports various code quality metrics, allows you to monitor trends, has an add-in that integrates with Visual Studio, allows you to write custom queries, and has a very good diagnostic facility.
Key Features:
-
This tool supports a large number of code metrics and allows for dependency visualization using directed graphs and a dependency matrix.
-
The tools also compare code base snapshots and validate architectural and quality rules.
-
LINQ queries can be used to create user-defined rules.
-
CQLinq is the name given to this possibility. In addition, the tool includes a large number of predefined CQLinq code rules.
Cost:
The package starts from $499 per year.
21. Klocwork

In addition to detecting semantic and syntax errors, Klocwork allows users to detect vulnerabilities in the code. This tool works well with many popular IDEs, including Eclipse, Visual Studio, and Intellij IDEA. This can be run concurrently with code creation; it performs a line-by-line check and includes a feature for addressing defects immediately.
Key Features:
-
Klocwork aims to integrate with CI/CD tools, packaging, cloud services, and machine provisioning, allowing for easy automated security testing.
-
CWE, OWASP, CERT, PCI DSS, DISA STIG, and ISO/IEC TS 17961 are all security standards.
-
Exceptions and many more are detected as bugs, quality issues, and code smells.
Cost:
Exceptions, as well as many others, are identified as bugs, quality issues, and code smells.
22. Cppcheck

Another free C/C++ static analysis tool. Cppcheck’s integration with other development tools such as Eclipse, Jenkins, CLion, Visual Studio, and others is a plus. Its installer is available at sourceforge.net.
Key Features:
-
Cppcheck supports a wide range of static checks that the compiler may not support. These are static analysis checks that can be run at the source code level.
-
The program is geared toward rigorous static analysis checks rather than heuristic checks.
-
A one-of-a-kind code analysis that detects various types of bugs in your code.
Cost:
Cppcheck is free software distributed under the terms of the GNU General Public License.
23. Helix QAC
Helix QAC is an excellent static analysis testing tool for Perforce C and C++ code (formerly PRQA). The tool has a single installer and works on platforms such as Windows 7, Linex Rhel 5, and Solaris 10. This provides very clear diagnostics, assisting in the identification of the root cause and the quick resolution of defects.
Key Features:
-
The Helix QAC dashboard is a centralized repository of analysis results that can be accessed via a web browser.
-
The results are uploaded to the dashboard in the form of snapshots.
-
Because of the customizable views and reports, project code quality and compliance metrics can be tracked over time.
-
The Helix QAC dashboard is fully customizable, allowing you to tailor its rows and columns to better meet the needs of your team and project.
Cost:
The package starts at $29 per user.
24. Goanna

Goanna is a C/C++ security static analysis tool that integrates with Microsoft Visual Studio, Eclipse, Texas Instruments Code Composer, and many other IDEs. This can be run as a compiler, allowing it to analyze file-level details as well as entire projects. It also has a great error reporting feature.
Key Features:
-
Goanna Studio integrates the Goanna technology directly into the Eclipse IDE, bringing the power of deep static C/C++ source code analysis to the fingertips of software developers.
-
It is built on the same advanced formal analysis engine that powers Goanna Central.
-
It includes over 300 check classes, including deep safety vulnerability analysis, CWE categorizations, and MISRA verifying.
Cost:
You can request a quote on their website.
25. Polyspace

Polyspace bug-finder aids in the detection of C/C++ defects; it is integrated with Eclipse and adheres to coding rule standards such as MISRA C, MISRA C++, and JSF++.
Key Features:
-
Polyspace Code ProverTM is a reliable static analysis tool that validates C and C++ source code for overflow, divide-by-zero, out-of-bounds array access, and other run-time errors.
-
It generates output without the need for program execution, code instrumentation, or test cases.
-
It can be used to validate either handwritten or generated code or a combination of the two.
-
Each code statement is color-coded to indicate whether it contains no run-time errors, has been proven to fail, is unreachable, or is unproven.
Cost:
The package starts at $29 per month.
26. Sourcemeter
Sourcemeter is a tool for analyzing C/C++, Java, C#, RPG, and Python code. Another advantage of this tool is that it can be integrated with free static checker tools such as cppcheck, PMD, and FindBugs. This tool's basic version is free, but it has fewer features. You can decide whether the free version meets the requirement or not based on your needs.
Key Features:
-
Accurate and deep static analysis, creation of full semantic graphs with semantic edges (calls, references), comments, and so on.
-
The plug-in runs SourceMeter from the SonarQube platform and uploads SourceMeter's source code analysis results to the SonarQube database.
-
The plug-in is compatible with the C/C++, Java, C#, Python, and RPG programming languages.
Cost:
You can request a quote on their website.
27. ConQAT
ConQAT is an outstanding tool for detecting clones. offers a variety of features, allows assimilation with other static analysis software, and includes a dashboard that displays details on issues discovered as well as other quality metrics.
Key Features:
-
ConQAT is built on pipes and filters architecture that allows for flexible complex analysis configurations through the use of a graphical configuration language.
-
For software systems, integrated visualization of various quality characteristics is used.
-
Quality dashboards can be created in a variety of ways, depending on the needs of the project.
-
Integration of a command-line interface into build software solutions integration toolkits (e.g Hudson, CruiseControl)
Cost:
You can request a quote on their website.
28. JArchitect
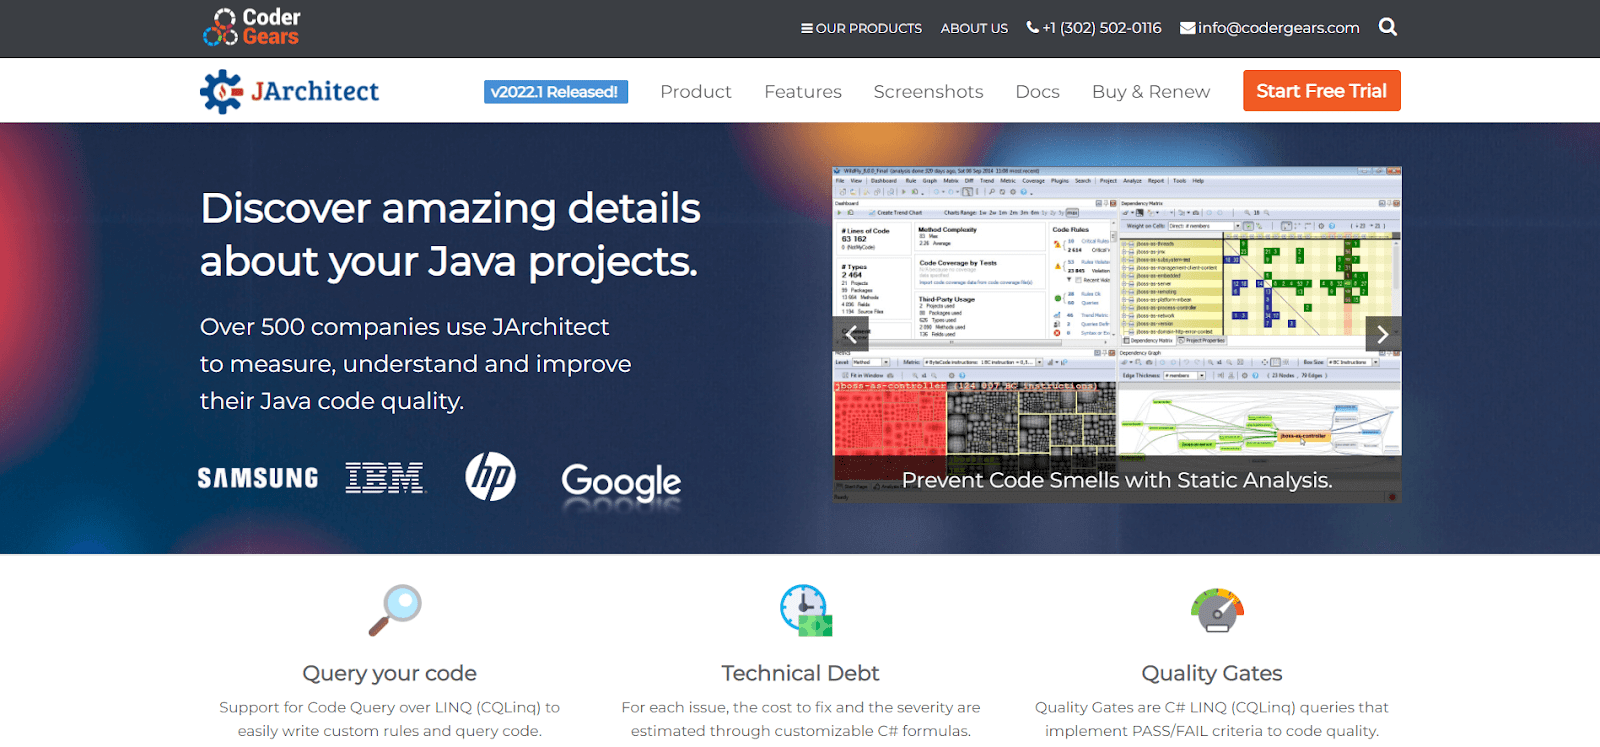
JArchitect, an excellent tool for analyzing Java code that supports Code Query over LINQ provides several code metrics, allows code comparison between builds, and includes a highly customizable reporting feature.
Key Features:
-
JArchitect is a Java code static analysis tool. This tool includes a large number of code metrics and enables dependency visualization using directed graphs and a dependency matrix.
-
The tools also compare code base snapshots and validate architecture and design and quality rules.
-
LINQ queries can be used to create user-defined rules.
Cost:
The package starts at $2999 per year.
29. OCLint

OCLint is a standalone tool for analyzing C/C++ and Objective-C programs that runs on Linux and Mac OS X. It does everything a static analysis tool is supposed to do, such as finding bugs, unused code, and redundant code, and it also comes with a highly customizable configuration that allows users to tailor it to their specific needs.
Key Features:
-
OCLint is a static code analysis tool that inspects C, C++, and Objective-C code to improve quality and reduce defects.
-
There are also lint-based rules, such as the number of lines without a statement, the number of boundaries in a method, and the number of lines/methods in a class.
Cost:
You can request a quote on their website.
30. Watchtower
Watchtower tool is primarily used by security professionals who want to perform manual code reviews. It works best on the local system, but it can also scan remote websites. Maintains a large configuration file, allowing different reporting options to be configured. The creation of alternate configuration files aids in the execution of multiple projects at the same time.
Key Features:
-
Watchtower is used by programmers to make quick work of finding and fixing bugs. Detailed stack traces and environmental information shorten software QA and development time.
-
Since the last deployment, project managers can track application reliability and error rates.
-
Apdex, reliability, and customer loyalty scores make it simple to monitor all critical aspects of application performance.
Cost:
You can request a quote on their website.
31. Cloc

Cloc supports multiple languages and allows the user to find blank lines, comment lines, and physical lines. Overall, an easy-to-use tool with useful features such as output in multiple formats that runs on multiple systems and comes with a simple installation package.
Key Features:
-
It is available in all major Linux distributions, supports a variety of programming languages and file extensions, and has no special requirements for use.
-
There is a simple and effective tool called "cloc – count lines of code" that allows you to rely upon all of your code while excluding comments and blank lines.
Cost:
You can request a quote on their website.
32. Rosecheckers
Rosecheckers is a tool that can be used to ensure that the developed code is compliant with CERT coding rules. SourceForge is where you can get it for free. This tool checks for C/C++ codes and occasionally find problems that other static analysis tools miss, but it cannot be considered a full-fledged standalone tool due to its inability to fully test because it is only a prototype.
Key Features:
-
Rosecheckers also goes beyond traditional tools to identify design alignment issues, onboarding risks, and aspects of the data on the enterprise and people's sides of the system.
-
Rosecheckers ultimately integrates the CI / CD pipeline to function as an extra team member that predicts risk to deliver and provides context-aware top-notch gates to track the wellbeing of the code.
Cost:
You can request a quote on their website.
33. IBM Rational Software Analyzer
IBM Rational enables the customer with a variety of tools, one of which is a software analyzer, that can be used for static code analysis. This tool is built on an extensible structure and works well with other Rational products.
Key Features:
-
Rational Software Analyzer Developer Version is a dynamic testing component that allows code analysis and bug recognition at the developer tier very early in the process.
-
Quality Improvement: RSAR will improve product quality by detecting flaws at the earliest stages of the Software Development Life Cycle (SDLC).
-
Lower Development and Defect Costs: By identifying bugs early in the SDLC, RSAR will lower your development, build, support, testing, and quality management costs.
Cost:
You can request a quote on their website.
34. Eclair

Eclair static analysis tool is very flexible and easy to configure, and it works on almost all platforms, including Windows, UNIX, Linus, and Mac OS X.
This tool can verify conformance against a variety of coding standards as well as other coding standards such as proprietary and project-based standards.
Key Features:
-
It detects or proves the absence of certain run-time errors in source code using formal methods-based static code analysis techniques such as abstract interpretation and model checking combined with constraint satisfaction techniques.
-
In terms of program analysis and verification, ECLAIR can statically detect or prove the absence of run-time anomalies as well as automatically check for conformance with several coding standards, including MISRA C, MISRA C++, CERT C Secure Coding Standard.
Cost:
You can request a quote on their website.
35. OWASP Orizon
OWASP Orizon is a tool that a security specialist can use to perform code reviews from a security standpoint. It also includes a set of APIs that can be used in conjunction with security tools to just provide code review services.
Key Features:
-
Owasp Orizon is a static open source analyzer method for investigating security flaws in Java programs.
-
The first stage of security analysis focuses on vulnerabilities in third-party libraries. Owasp Orizon will attempt to comprehend target package dependencies before looking for known security issues.
-
There have been no reports of vulnerabilities in OWASP Orizon or its dependent libraries.
Cost:
You can request a quote on their website.
36. PMD

PMD is a free and open-source code analyzer that supports C/C++, Java, and JavaScript. This is a simplified tool for detecting common flaws. In addition, it detects code duplication in Java.
Key Features:
-
PMD is a free and open-source rigid source code analyzer that discloses issues discovered in application code.
-
PMD has built-in rule sets as well as the ability to write custom rules.
-
It supports Java, Apex and Visualforce, PLSQL, Apache Velocity, JavaScript, XML, and XSL files.
-
Issues reported by PMD are typically inefficient code or bad programming habits that, if accumulated, can reduce the program's performance and maintainability.
Cost:
You can request a quote on their website.
37. FindBugs

FindBugs is a free tool for locating bugs in Java code. It works with any Java version but needs JRE (or JDK) 1.7.0 or afterward to run.
Key Features:
-
FindBugs is a free and open-source static code analyzer that detects potential bugs in Java programs.
-
FindBugs works with bytecode rather than source code.
-
The software is scattered as a stand-alone graphical user interface (GUI) application.
-
It also provides suggestions for how to resolve the issue during development.
-
When compared to other static code analyzing tools that we used, the number of false-positive issues raised in finding bugs was low.
-
The time required for the source code analysis was also very short.
Cost:
You can request a quote on their website.
38. Flawfinder

Flawfinder is an open-source tool that is primarily used to identify security flaws in C/C++ programs. It can be downloaded, installed, and run on UNIX-like systems.
Key Features:
-
Flawfinder is simpler to use; simply enter a directory name, and flawfinder will recursively enter the directory, figure out what needs to be analyzed, and analyze it.
-
Other advantages of flawfinder include the ability to handle internationalized programs.
-
Flawfinder's automated recursion and HTML formatted results make it ideal for source code hosting systems.
Cost:
You can request a quote on their website.
39. Splint
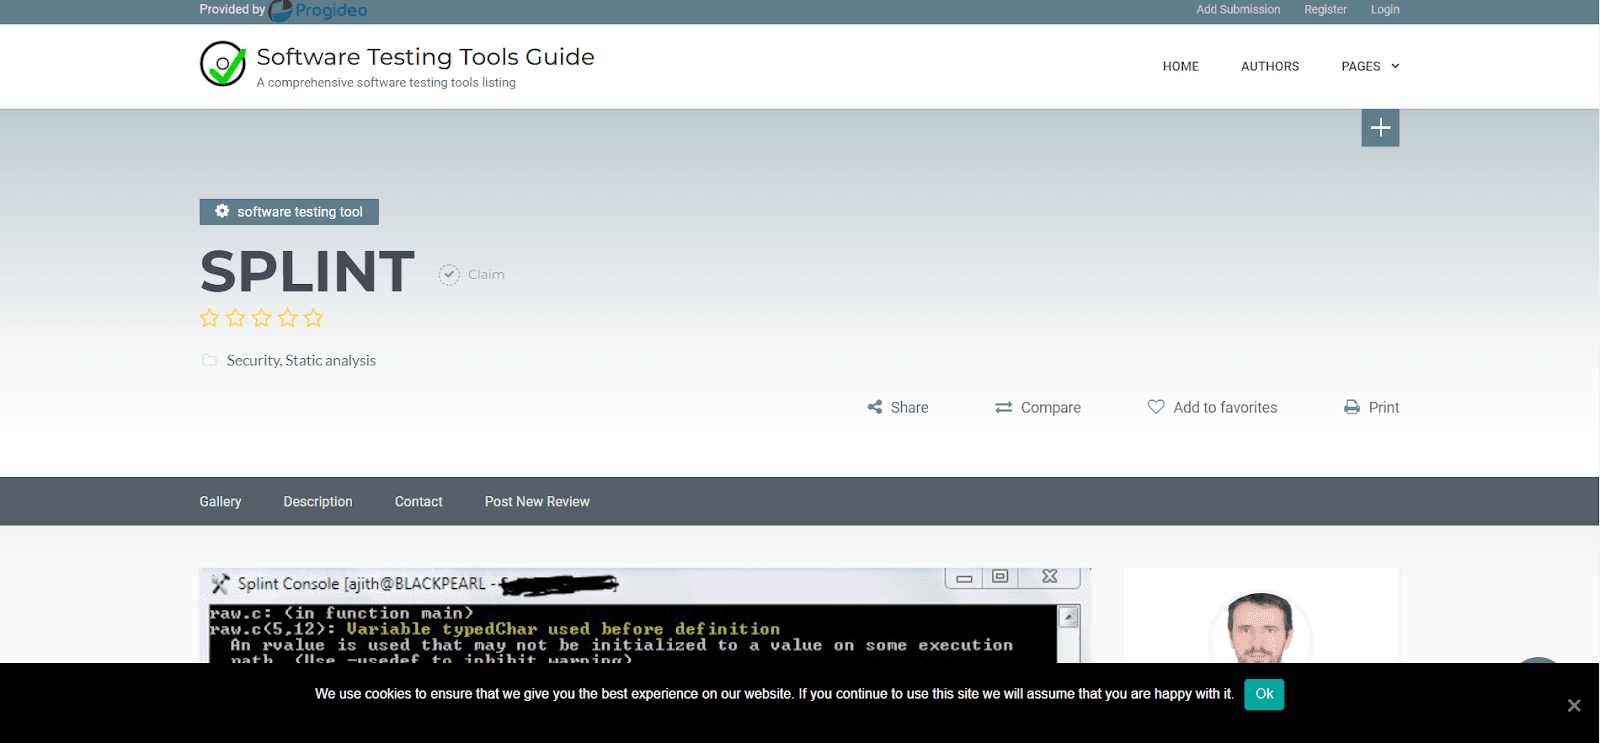
The splint is a static and security analysis tool for C programs that are open source. It comes with the most basic features, but with the addition of additional annotations, it can perform similarly to any other standard tool.
Key Features:
-
A Splint is a programming tool that checks C programs statically for security vulnerabilities and coding errors.
-
The splint can interpret special annotations to source code, allowing it to perform stronger checks than is possible simply by looking at the source.
-
GPSD employs splint as part of its effort to design for zero defects.
-
The splint is free software licensed under the GNU General Public License.
Cost:
You can request a quote on their website.
40. DeepScan

DeepScan is a sophisticated static analysis tool that supports JavaScript, TypeScript, React, and Vue.js.
Instead of coding conventions, DeepScan can be used to detect potential runtime errors and quality issues. Integrate with your GitHub repositories to gain a thorough understanding of your web project.
Key Features:
-
DeepScan is a static code analysis tool and server-based service used to inspect JavaScript code. Using data-flow analysis, it checks for potential run-time errors and poor code quality.
-
It examines the program's execution and data flow in greater detail. This allows syntax-based linters to detect issues that syntax-based linters cannot. As a result, you can prioritize major issues first and then move on to minor issues.
Cost:
You can request a quote on their website.
Things To Consider While Selecting Static Code Analysis Tools
Lowers The Risks Associated
Code bases are rapidly growing and becoming more complex as software becomes more critical to delivering product value. Internal and outsourced development teams work together to create code all over the world. Large legacy codebases that are reused and modified for current applications are combined with new code.
While reusing code can save money, it can also increase complexity and increase the risk of errors. While outsourcing development has its benefits, it also adds variability and complexity to a project. Static analysis tools address this complexity and the risk it entails on multiple fronts.
Security Is Improved And Vulnerabilities Are Reduced
Because of the increasing reliance on embedded software, security considerations during software design are becoming increasingly important. Buffer overflows, resource leaks, insufficient encryption, insecure interfaces, and other defects and security issues continue to plague embedded systems.
Since more devices are implemented and linked to the Internet of Things, the percentage of entry and exit points for hackers grows significantly. Static analysis ensures coding consistent quality and is an effective technique for identifying common security vulnerabilities such as system vulnerabilities and resource leaks.
Process Streamlining
The static analysis provides constructive criticism to development companies, enabling better probably great habits and creating compelling code faster. Tools that provide well-documented comments to fix a potential hazard and can pinpoint the exact line of code in which the defect occurred assist developers in understanding their inconsistencies in the frame of reference of what they were seeking to accomplish.
If development teams receive regular feedback, they are more highly probable to learn from the experience and avoid similar situations in the future. The quicker development teams learn about difficulties, the making it much easier for they can be fixed. Static analysis, as opposed to testing results, which happens weeks or months after the software is executed, can be implemented while the software is being written.
Early Detection And Remediation Saves Time
The design to monitor errors without running software is the most significant distinction among both static analysis and other testing methods. Defect detection without executing the program is particularly useful in embedded applications, where complete and accurate runtime assessment for such errors is commonly ineffective, if not impossible. There is no need to splurge weeks setting up and configuring dozens of static analysis test cases. This type of analysis also helps software developers detect inconsistencies that test automation, system testing, quality management, and manual coding standards typically miss.
Conclusion
In 2026, the best static code analysis programs are the ones teams actually run continuously, with results that are actionable and tied to engineering workflows. Poor software quality carries enormous business cost, and industry reporting estimates it at over $2.41 trillion annually in the United States alone, with a large share linked to cybercrime driven by insecure code. The bottom line is that static analysis is most effective when it is automated, integrated into CI, and enforced with clear quality gates, so teams prevent high impact issues from shipping instead of discovering them after release.
FAQs
What are Static Code Analysis tools?
Under pressure, development teams benefit from static analysis. On-time delivery of high-quality releases was required. Coding and compliance requirements must be met. And making mistakes is not an option.
That is why static analysis tools are used by development teams. Source code analysis tools, also recognized as Static Application Security Testing (SAST) Tools, can aid in the analysis of source code or compiled versions of code in order to detect security flaws.
SAST tools can be incorporated into your IDE. Such tools can assist you in detecting problems during software development. When compared to vulnerability detection late in the design cycle, SAST tool feedback can save time and effort.
What should you consider while purchasing Static Code Analysis tools?
Here are some things to think about when deciding which tool is best for you:
Programming Language Analyzers are intended for use with a wide range of programming languages. As a result, it's critical to select a tool that supports your language.
- Standards
Amongst the most typical applications of static analyzers is to help make sure normative implications. As a result, if you work in a tightly controlled industry that requires a programming language, ensure that your tool endorses it.
- Choosing a Static Analysis Tool
Interested in learning more about selecting a static code analysis tool?
Here are things to consider while purchasing this brilliant tool:
-
The advantages and disadvantages of static code analysis.
-
Best practices for using it.
-
Perfect criteria to consider when selecting the right tool.
What Are the Advantages of Static Analysis Software?
There are several advantages to using static code analysis tools, especially if you need to meet an industry standard.
-
The perfect static code analysis devices are quick, thorough, and precise.
-
Manual code reviews take time for developers. Automated tools are significantly faster.
-
Static code checking identifies issues early on.
-
They also determine the precise location of the code error. As a result, you'll be able to rectify those mistakes faster. Besides this, earlier unearthed coding errors are less cost-prohibitive to correct.
-
Depth Testing is incapable of covering every possible code execution path. In contrast, a static code analyzer can.
The distinctions between open-source and commercial SAST tools?
When comparing pricing for SAST tools, consider how your development team is structured and works. However, companies do not always need to pay for SAST tools, especially at first.
There are numerous free scanners available. Begin with that and demonstrate its worth to your management. Some of the more advanced tools that have support gather a lot of information about your environment.
What are the new advances that have been made in testing javascript-based applications?
Code smells are correlations in the code base that potentially cause comprehension and mechanical problems in the program. When code smells are detected, they can be reverse-engineered to improve the quality construction of the code. The current state of the art in custom application code smell detection is limited, and the industrial resources available to software developers to sustain their code are primarily static monitoring systems, rendering them ineffectual for supporting JavaScript developers.
WARI, for example, investigates dependencies between JavaScript functions, CSS styles, HTML tags, and images. The goal is to find unused images, as well as unutilized and recreated JavaScript functions and CSS styles, statically.
